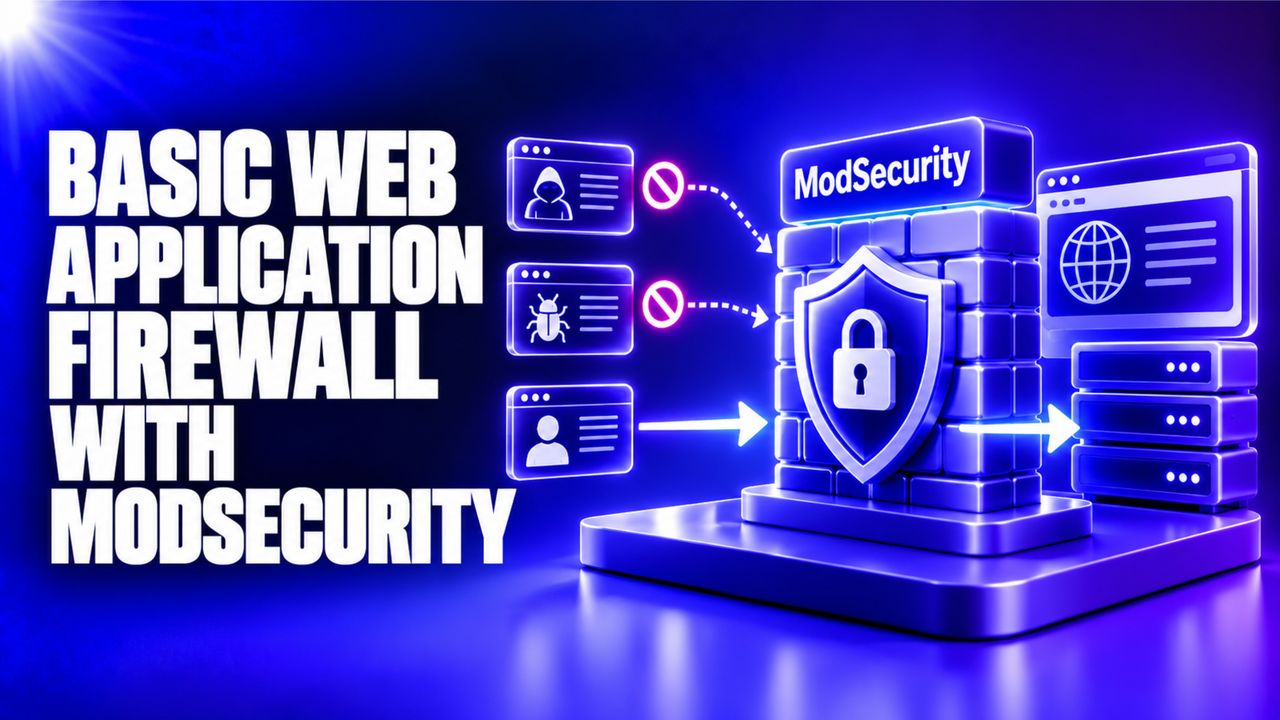
This short course is for Indian students and career switchers who want a practical security skill that can be added to a resume. You'll set up ModSecurity on Apache/Nginx, write simple rule sets, and test the firewall against common attacks.
By the end of the course you'll have a working WAF protecting a demo site and a collection of reusable rules you can adapt for any small web project.
After completing the course you’ll be able to install ModSecurity, tune rules, interpret logs, and explain WAF benefits to clients or employers.
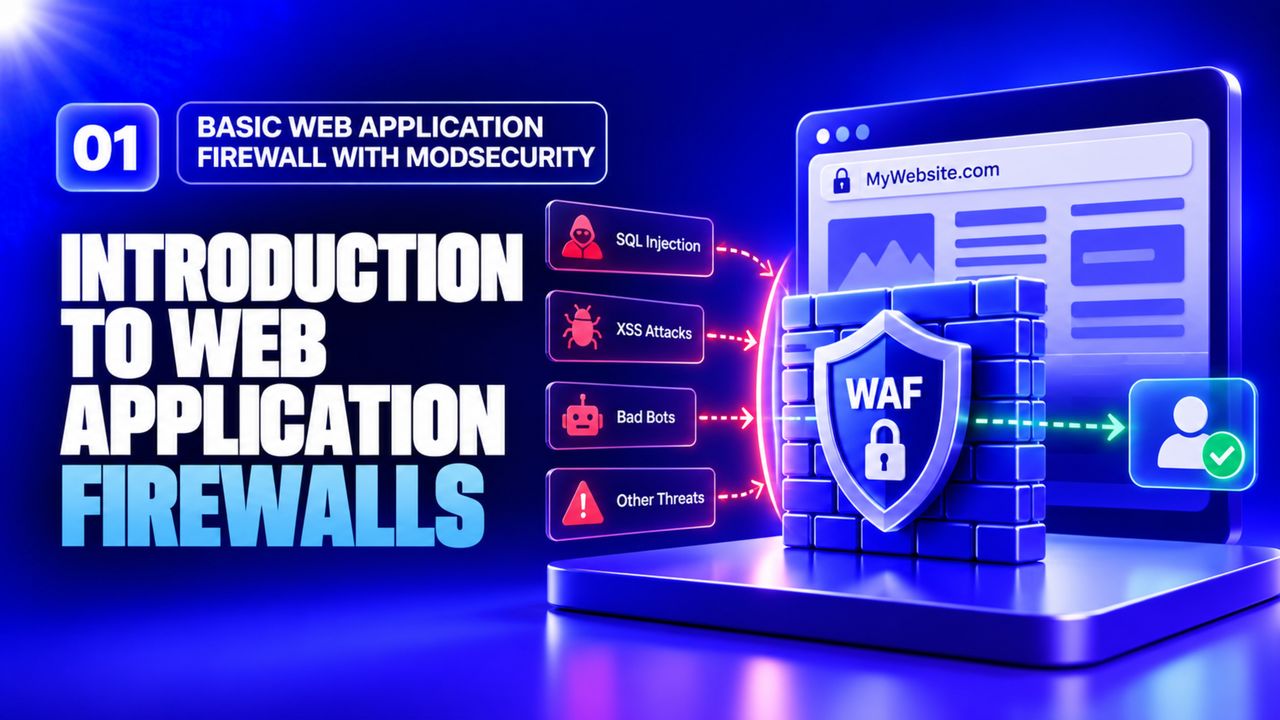 Introduction to Web Application Firewalls
F5 DevCentral Community · 10 min
2
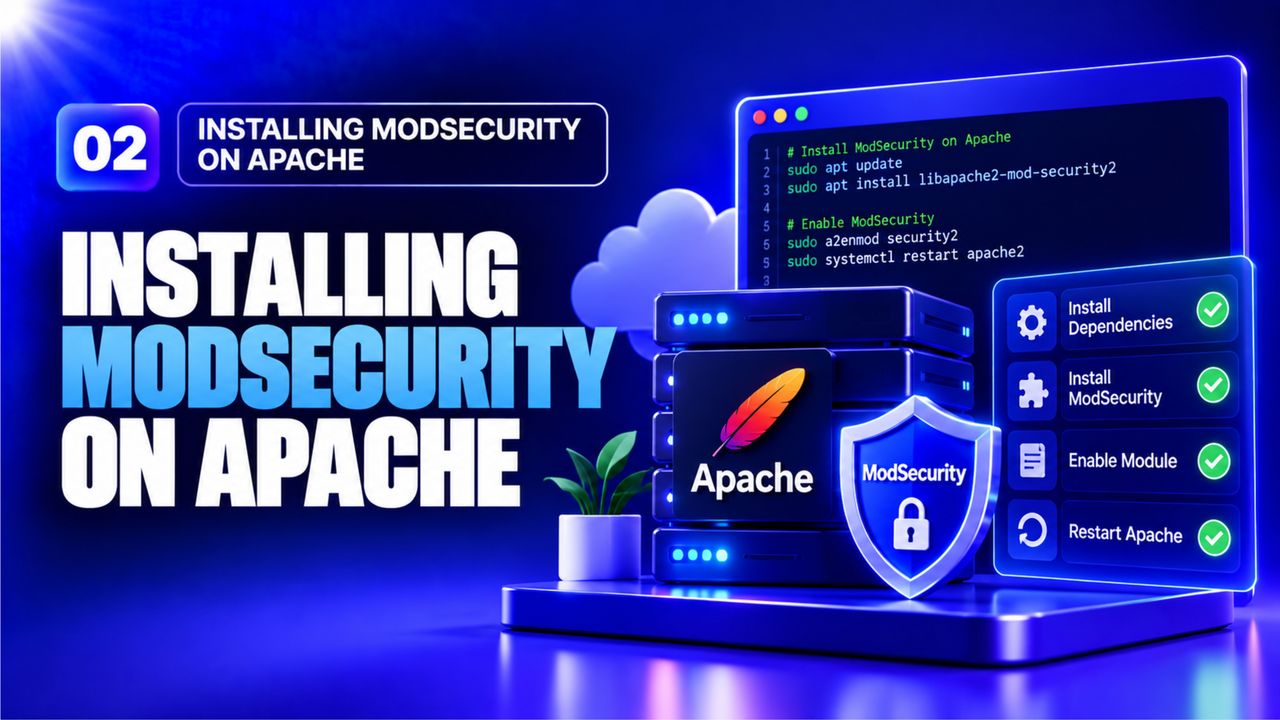 Installing ModSecurity on Apache
HackerSploit · 21 min
3
 Installing ModSecurity on Nginx
HackerSploit · 30 min
4
 Understanding the OWASP Core Rule Set (CRS)
nullcon · 44 min
5
 Creating a Simple Custom Rule – SQL Injection
MivoCloud · 4 min
6
 Hands‑On Project: Protect a Demo Site
HackerSploit · 21 min
7
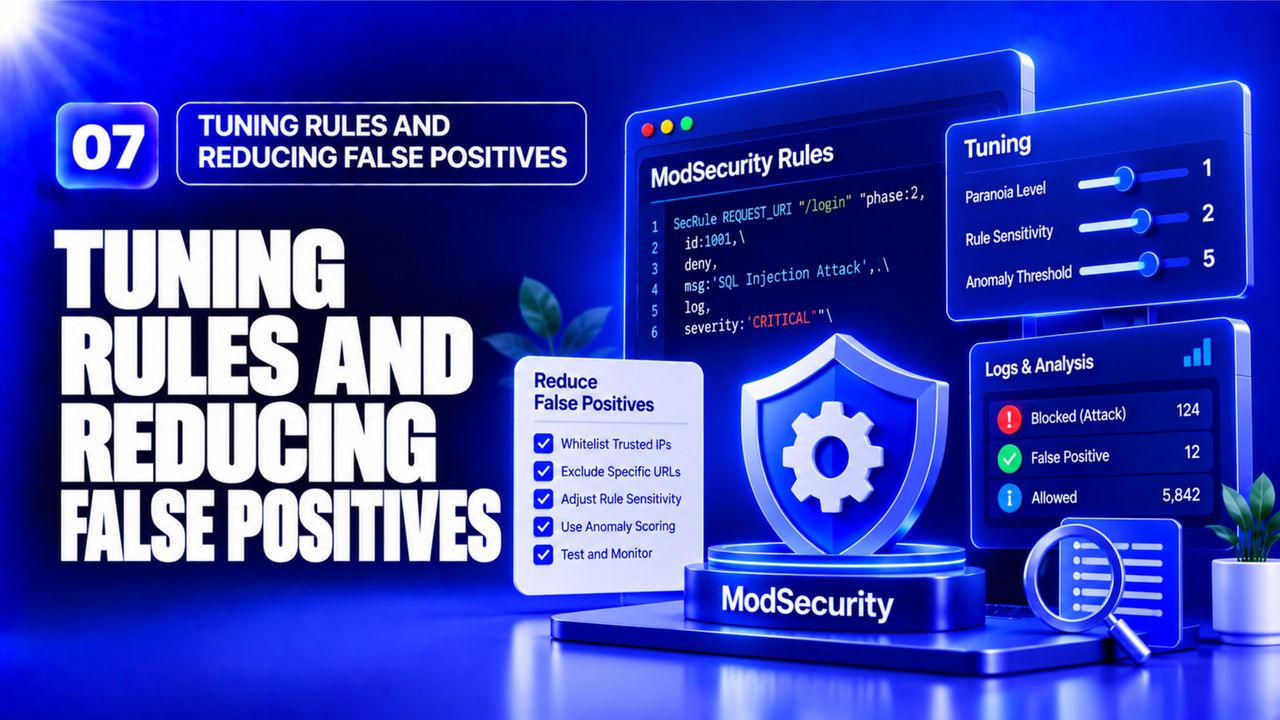 Tuning Rules and Reducing False Positives
Taylor Walton · 15 min
8
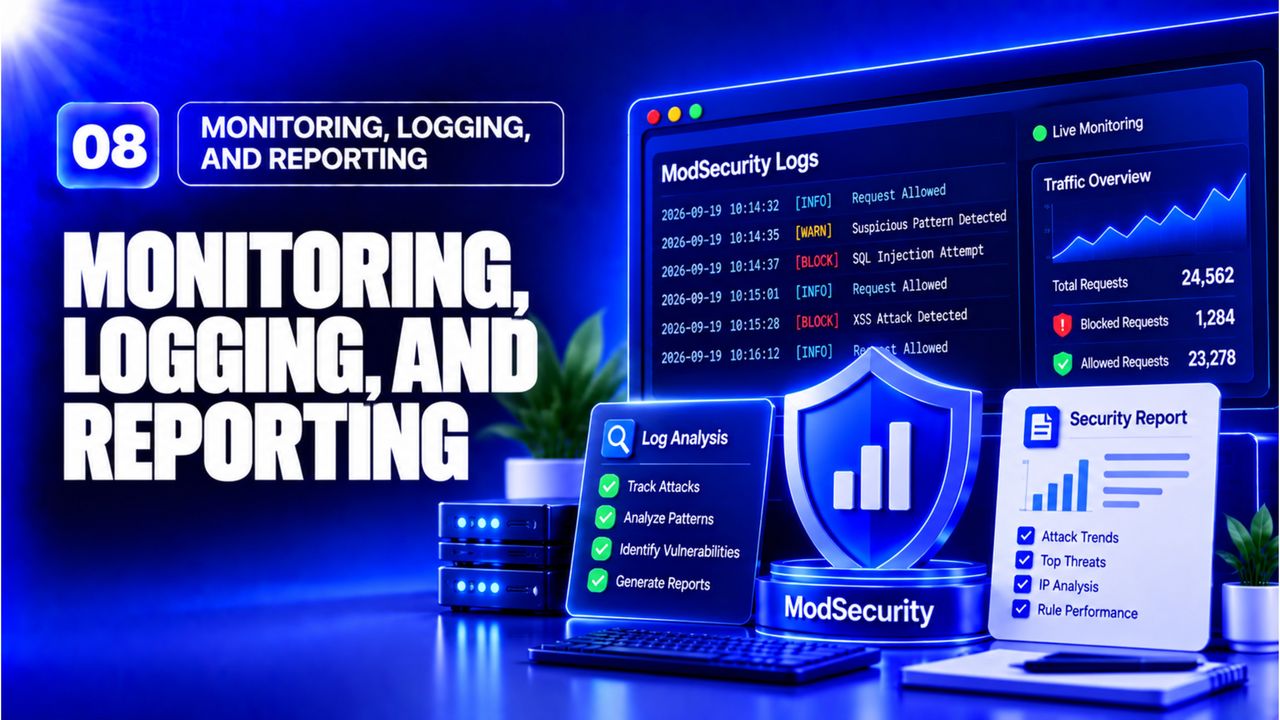 Monitoring, Logging, and Reporting
Techno Tim · 28 min
Create a small blog site (e.g., WordPress or a static site) behind ModSecurity on Apache or Nginx. Submit a GitHub repository link containing:
Reviewer checklist