Video by MivoCloud on YouTube · 4 min. We did not make this video and we do not host it — watching it here still counts as a view for the creator.
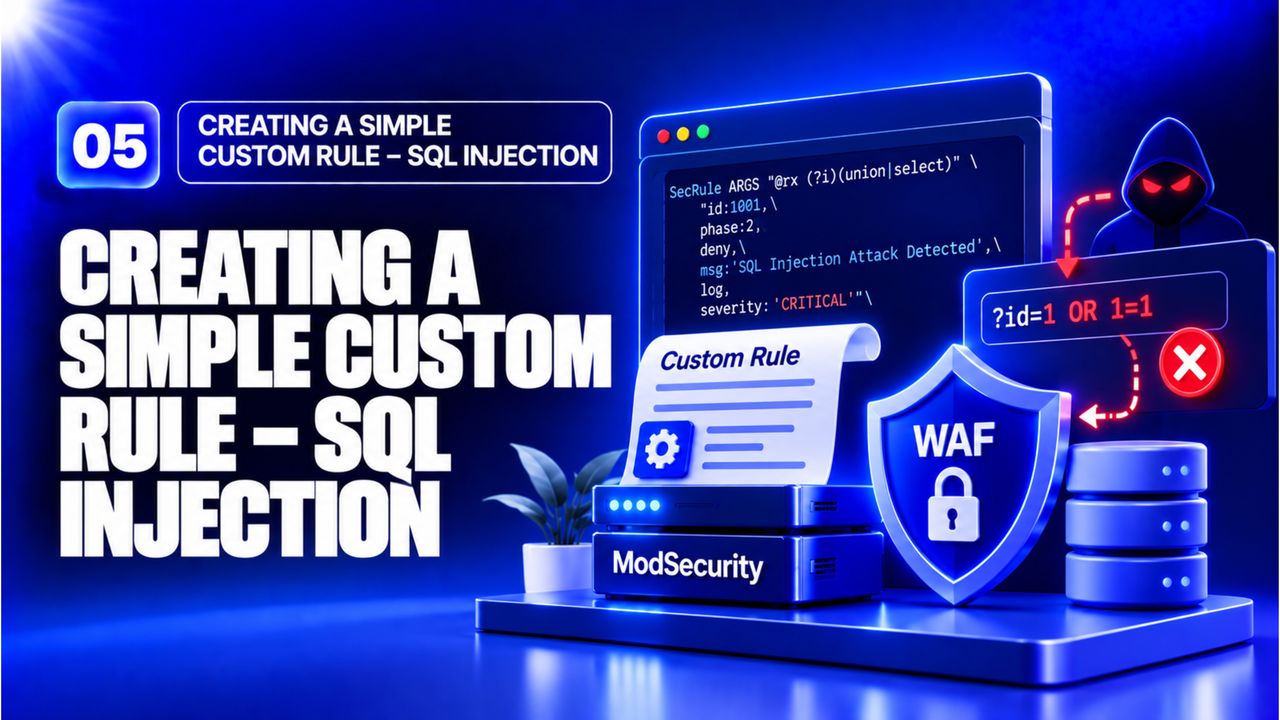
Write a rule that matches typical SQLi patterns like SELECT * FROM in query strings. Pay attention to the correct SecRule syntax and the use of TX:ANOMALY_SCORE. New users often forget the id parameter, which is required for rule management.
Custom rules let you protect app‑specific endpoints that the generic CRS may miss. Test the rule with a curl request containing a payload to see the log entry and the response code.
Sign in with your email, Google or GitHub. No password to remember. The same account carries your progress, your certificates and anything else you do with Nexgino later.
Sign in to continueIt takes about fifteen seconds.