Video by nullcon on YouTube · 44 min. We did not make this video and we do not host it — watching it here still counts as a view for the creator.
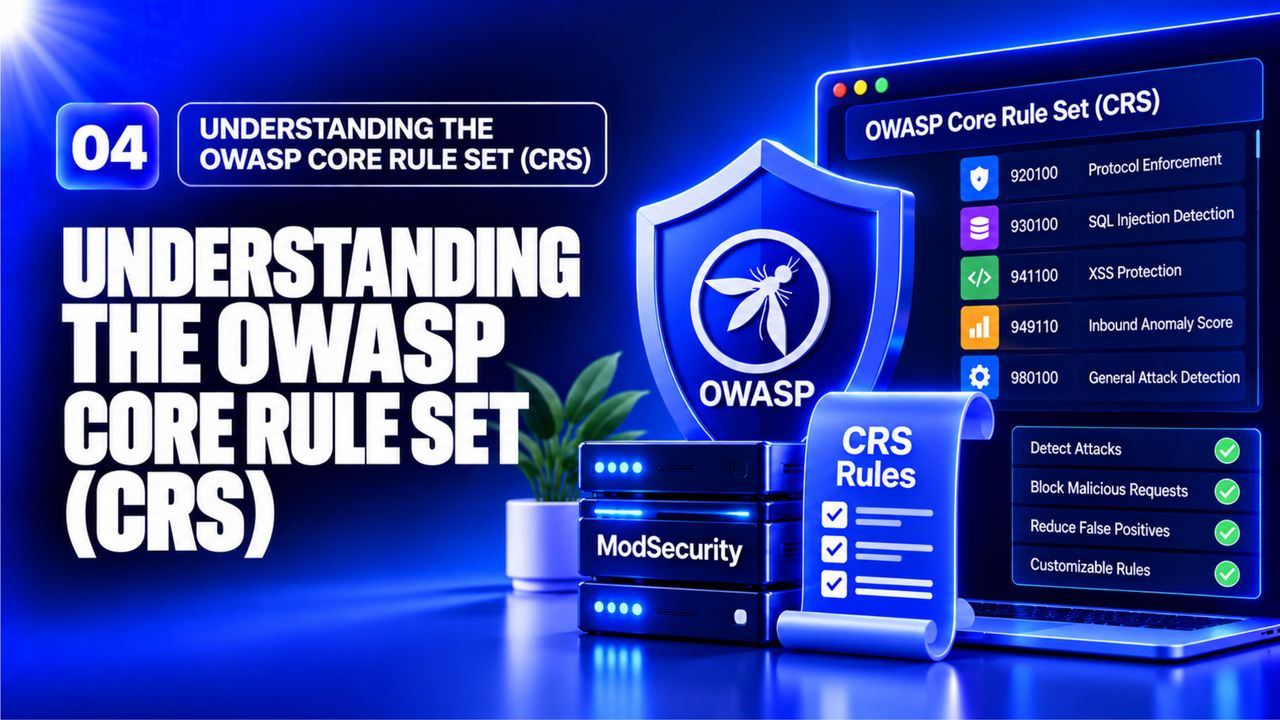
The CRS provides a ready‑made collection of generic attack signatures. Watch how the rules are grouped (e.g., REQUEST-942-APPLICATION-ATTACK-XSS). Beginners often enable the entire CRS without adjusting the anomaly scoring, which can cause false positives.
In practice you start with the base CRS, then disable or tune rules that interfere with your application’s legitimate traffic. Knowing the rule IDs helps you write exceptions later.
Sign in with your email, Google or GitHub. No password to remember. The same account carries your progress, your certificates and anything else you do with Nexgino later.
Sign in to continueIt takes about fifteen seconds.