Video by HackerSploit on YouTube · 21 min. We did not make this video and we do not host it — watching it here still counts as a view for the creator.
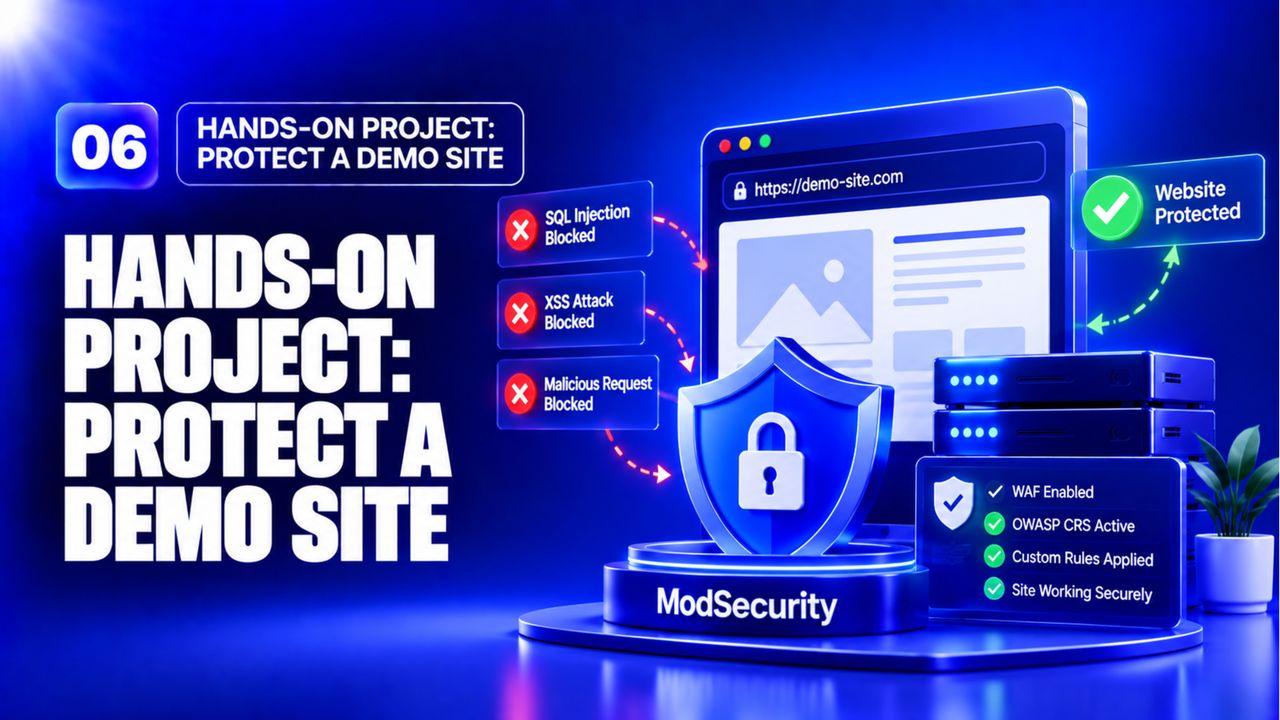
Set up a simple PHP or static HTML site on your local server and enable ModSecurity with the CRS and your custom SQLi rule. Use the OWASP Juice Shop or a vulnerable page to generate attacks. Beginners often forget to enable SecRuleEngine On after editing rules.
Run a few attack vectors (SQLi, XSS, path traversal) and verify they are blocked in the ModSecurity audit log. This exercise shows how logs translate to real security events and prepares you for troubleshooting in production.
Sign in with your email, Google or GitHub. No password to remember. The same account carries your progress, your certificates and anything else you do with Nexgino later.
Sign in to continueIt takes about fifteen seconds.