Video by Taylor Walton on YouTube · 15 min. We did not make this video and we do not host it — watching it here still counts as a view for the creator.
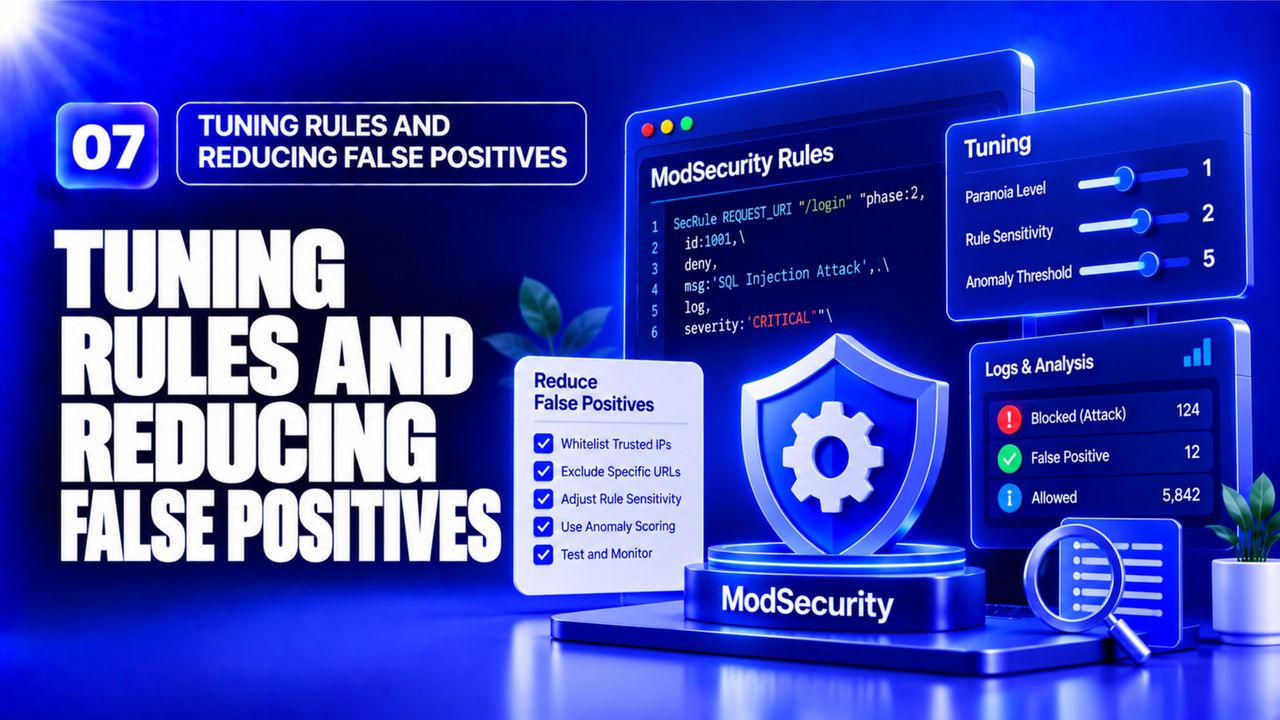
Learn to use ctl:ruleRemoveById and ctl:ruleRemoveTargetById to create exceptions for legitimate traffic. A common beginner mistake is disabling too many rules, which weakens protection. Focus on narrow exceptions, e.g., only for a specific URL path.
In real deployments you monitor the audit log, identify recurring false positives, and adjust the rule set accordingly. This iterative process keeps the WAF effective without disrupting users.
Sign in with your email, Google or GitHub. No password to remember. The same account carries your progress, your certificates and anything else you do with Nexgino later.
Sign in to continueIt takes about fifteen seconds.